How Pokodrop Protects Your Documents
Comprehensive overview of our Zero-Knowledge Client-Side Encryption, storage lifecycles, and privacy guarantees.
For Everyone: Simple Explanation
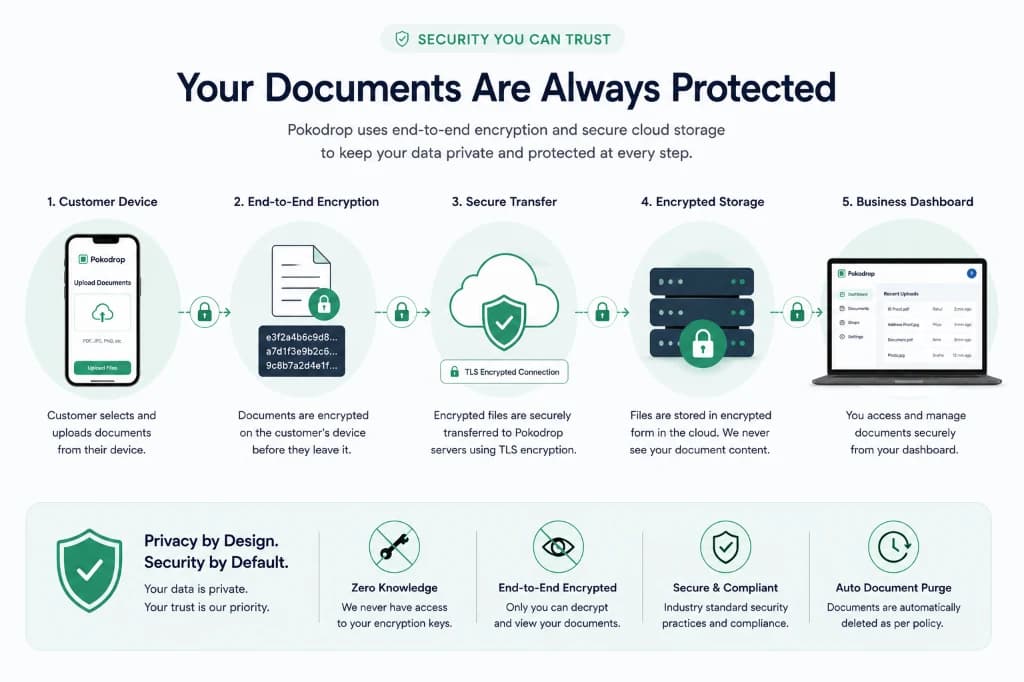
When you upload a document at a shop using Pokodrop:
Your files are locked with a digital key inside your phone's browser before being sent across the internet.
Pokodrop servers only hold locked cipher data. No employee or third party can view or read your documents.
Only the shop prints your file. Once printed, files are permanently erased with zero leftover copies.
For Technical Users: Cryptographic Specifications
1. Client-Side Web Cryptography API
Document encryption executes entirely within the client runtime using the standard W3C SubtleCrypto API. Each customer session generates an ephemeral 256-bit AES-GCM (Galois/Counter Mode) symmetric key. The file payload is divided into binary chunks, authenticated with a 128-bit authentication tag, and transmitted over TLS 1.3.
2. Asymmetric Key Exchange & Zero-Knowledge Storage
Each registered shop operator generates an asymmetric RSA-OAEP / ECDH keypair upon account creation. The customer's ephemeral AES key is encrypted with the shop's public key before upload. Consequently, only the authenticated shop operator holding the corresponding private key in browser memory can decrypt the payload. Pokodrop servers act purely as blind, zero-knowledge relays.
3. Automated Ephemeral TTL & Cryptographic Shredding
Ciphertext blobs are provisioned with short time-to-live (TTL) policies. When a shop operator clicks 'Purge Session', the metadata and cloud storage objects are immediately deleted via atomic API transactions, rendering any residual ciphertext permanently unrecoverable.
Because Pokodrop does not possess master decryption keys for customer documents, our support team cannot inspect or recover document contents once a session is purged or expired.